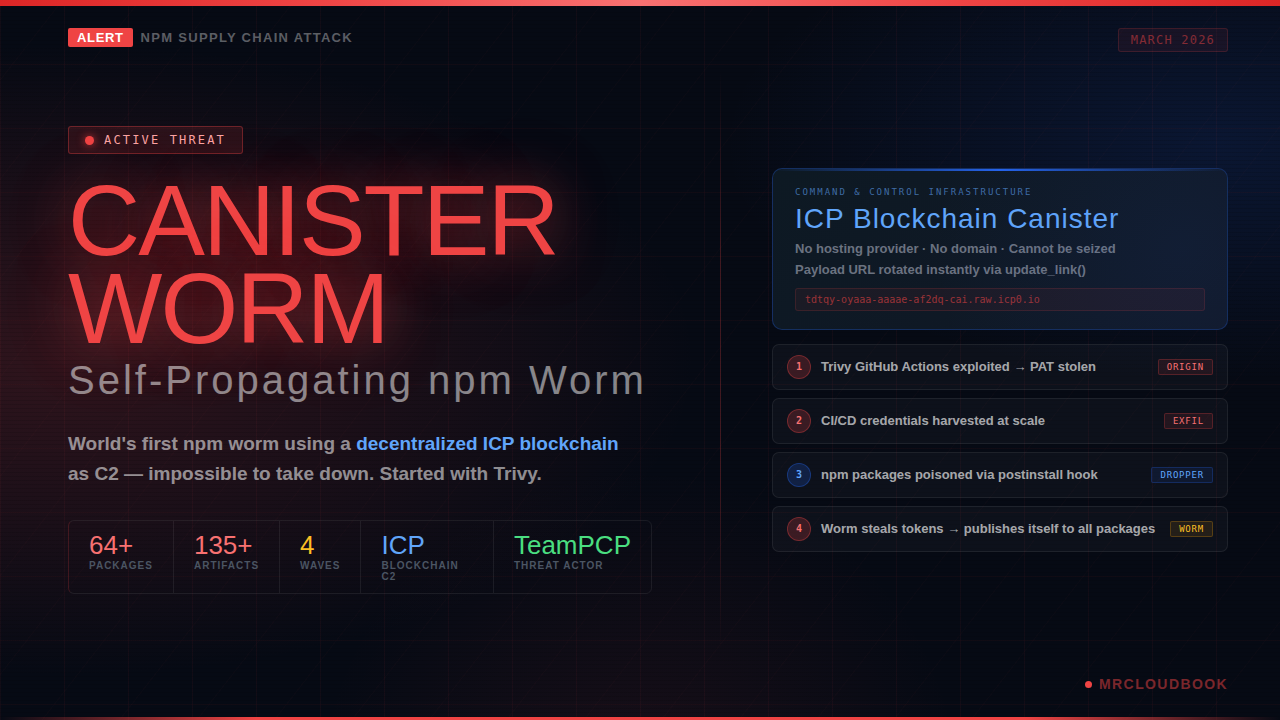
CanisterWorm The Self-Propagating npm Supply Chain Worm
CanisterWorm is a self-propagating malware that infected 64+ npm packages in March 2026. Named by Aikido Security and Socket.dev, it's notable for two historic firsts: …
Hands-on DevOps, Cloud, and Kubernetes tutorials - from setup to production.
CanisterWorm is a self-propagating malware that infected 64+ npm packages in March 2026. Named by Aikido Security and Socket.dev, it's notable for two historic firsts: …
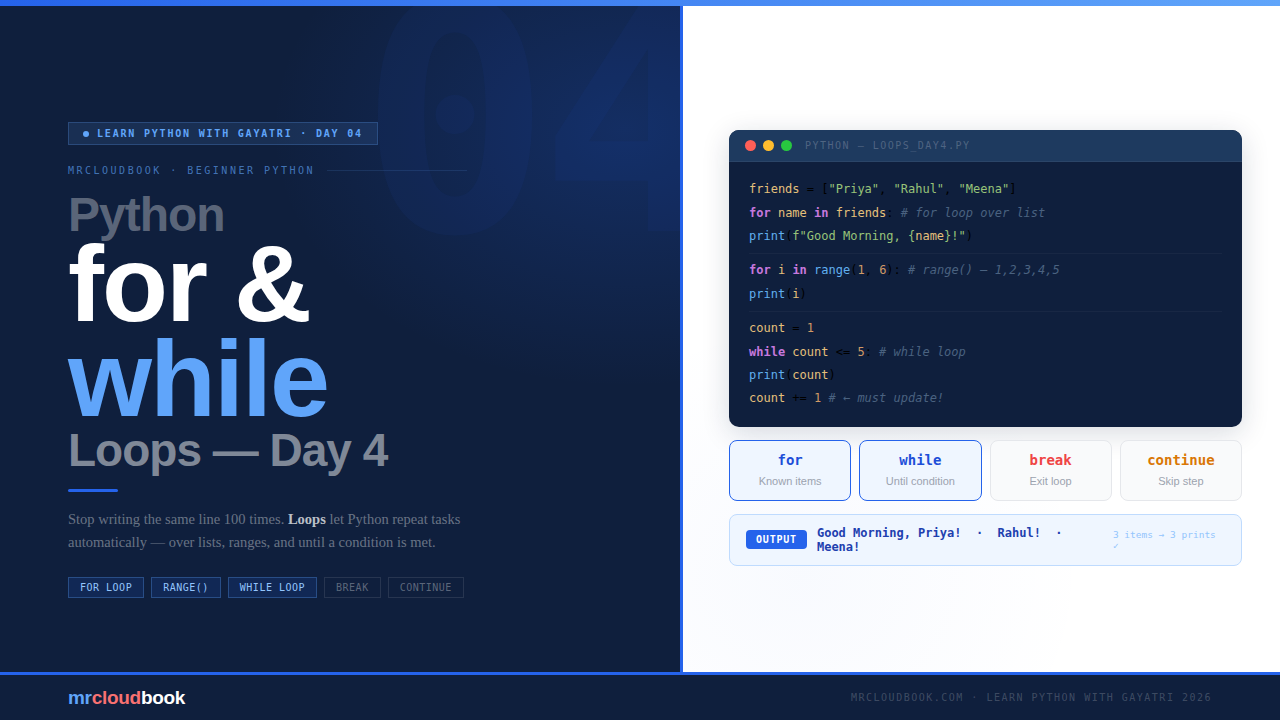
A loop tells Python: keep doing this thing, again and again, until I say stop. Without loops, repetitive tasks mean writing the same line over …
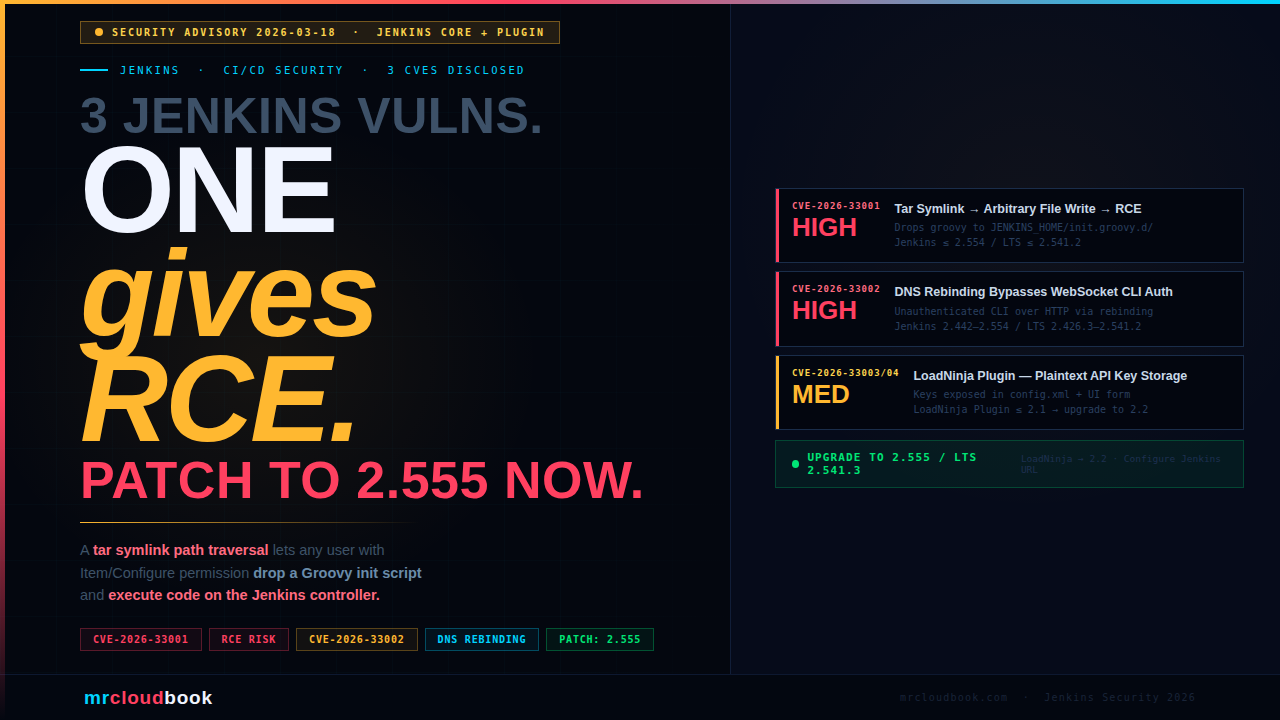
The Jenkins project released a security advisory on March 18, 2026, addressing three vulnerabilities - two rated High and one Medium. The most critical, CVE-2026-33001, …
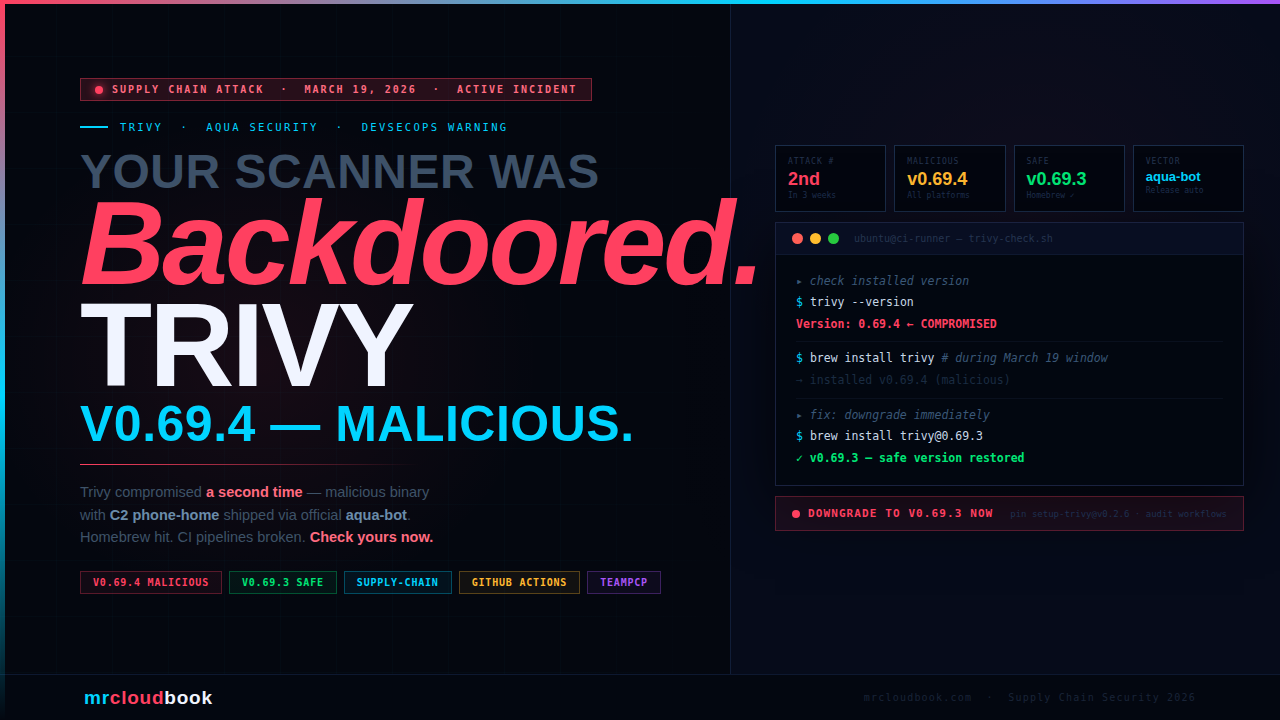
On March 19, 2026, Trivy - the most widely used open-source vulnerability scanner in DevSecOps pipelines - had its release process compromised for the second …
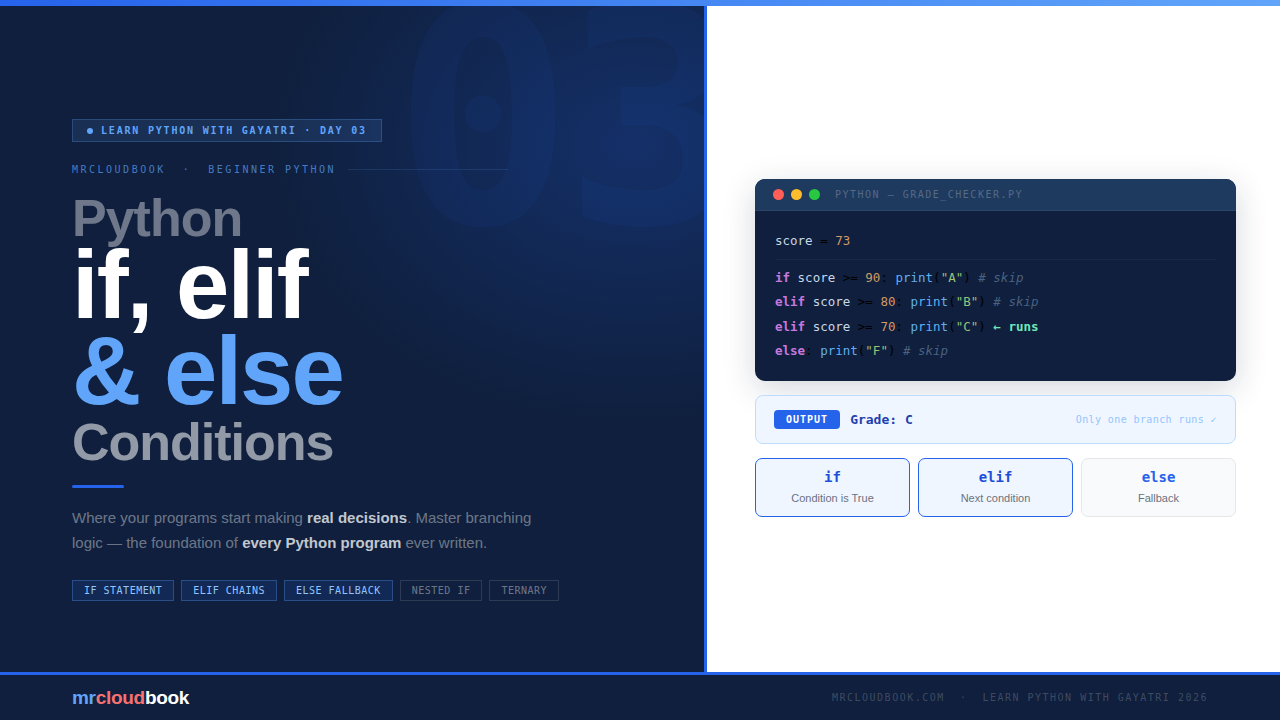
Every program worth writing needs to make decisions. Should the user be allowed to log in? Is a number even or odd? Did the form …
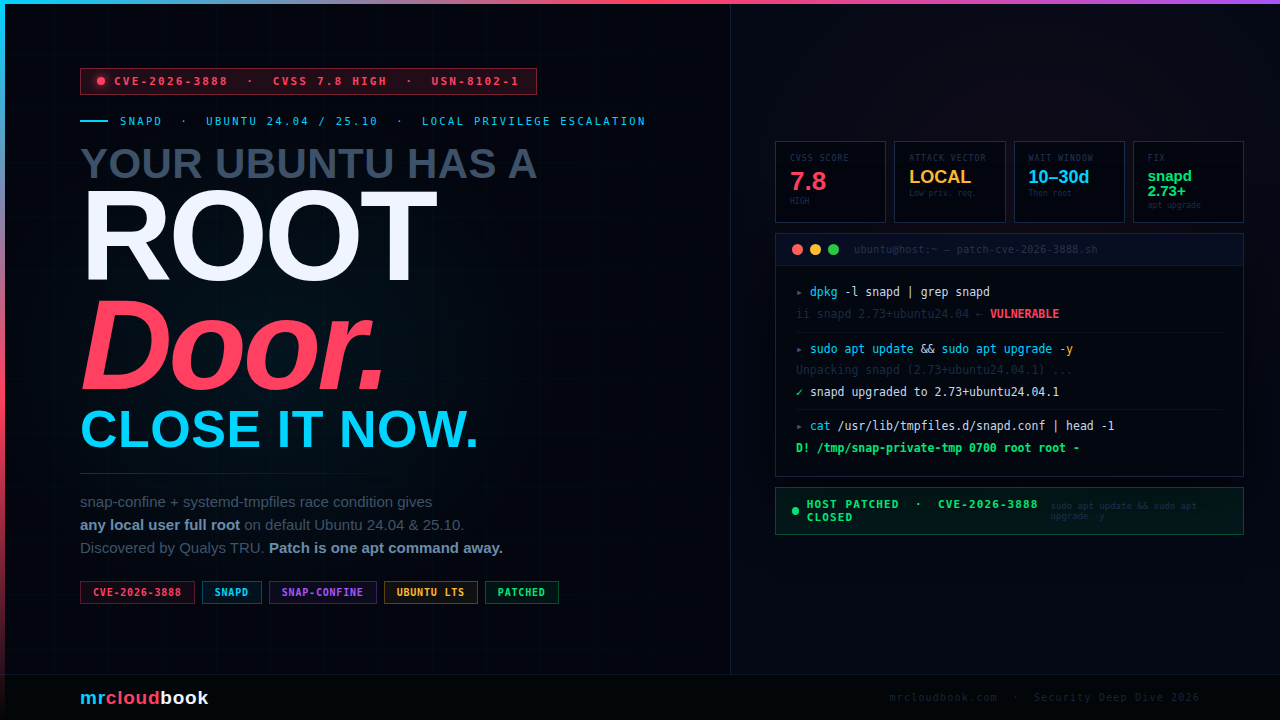
Qualys Threat Research Unit discovered that snapd incorrectly handles operations in the snap's private /tmp directory. When systemd-tmpfiles cleans this directory on its scheduled timer, …
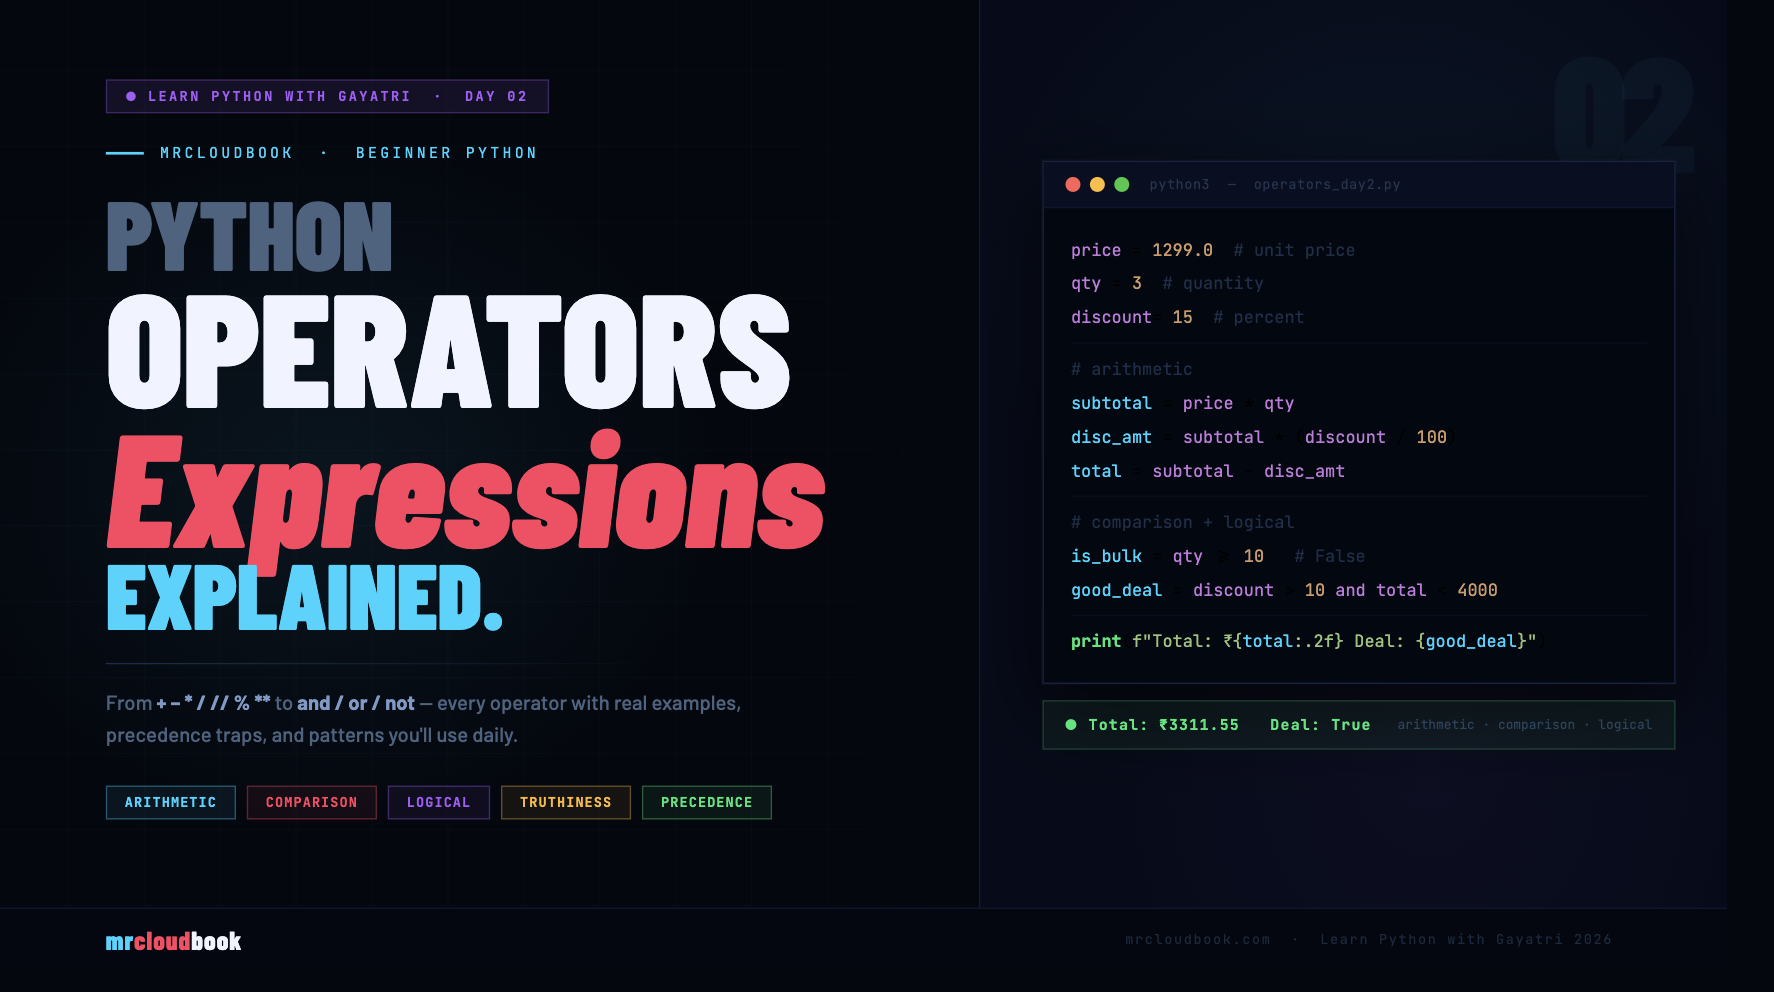
Mastering operators and expressions is like learning the grammar of Python; once you understand how these symbols interact, you can begin writing complex logic with …
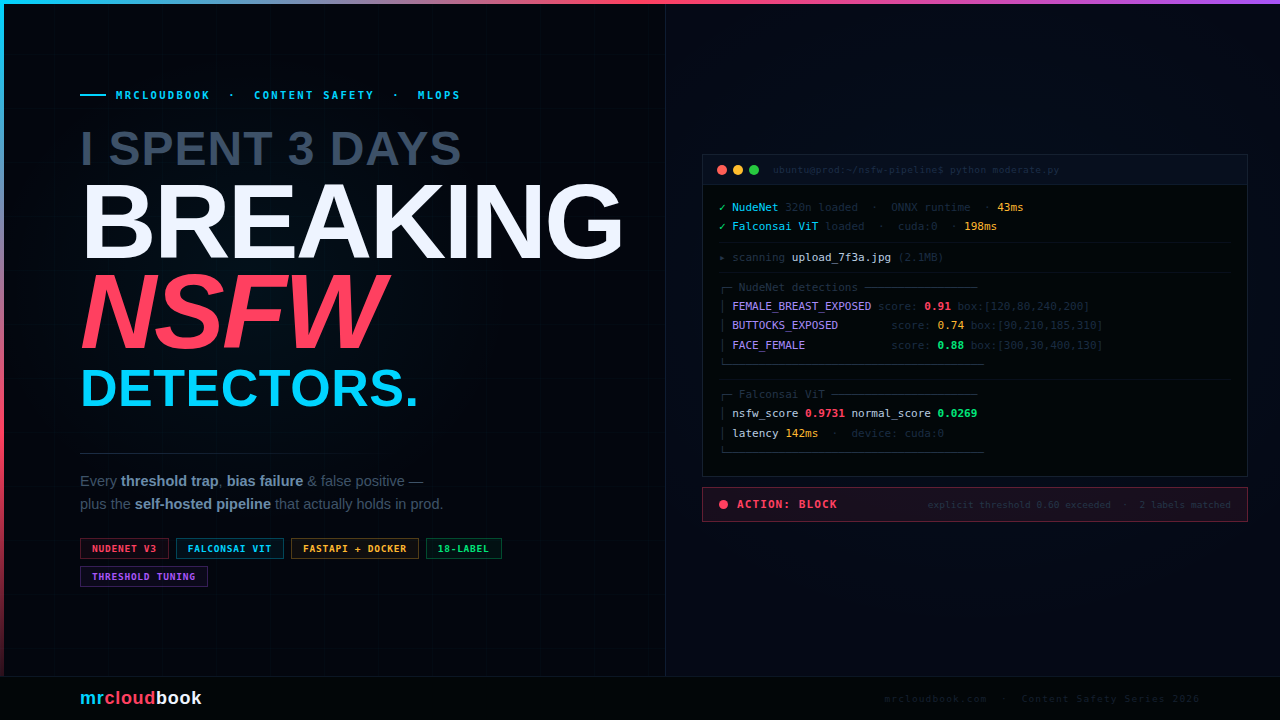
NSFW detection is one of those infrastructure problems that looks simple from the outside - just run a model on images, right? - and turns …
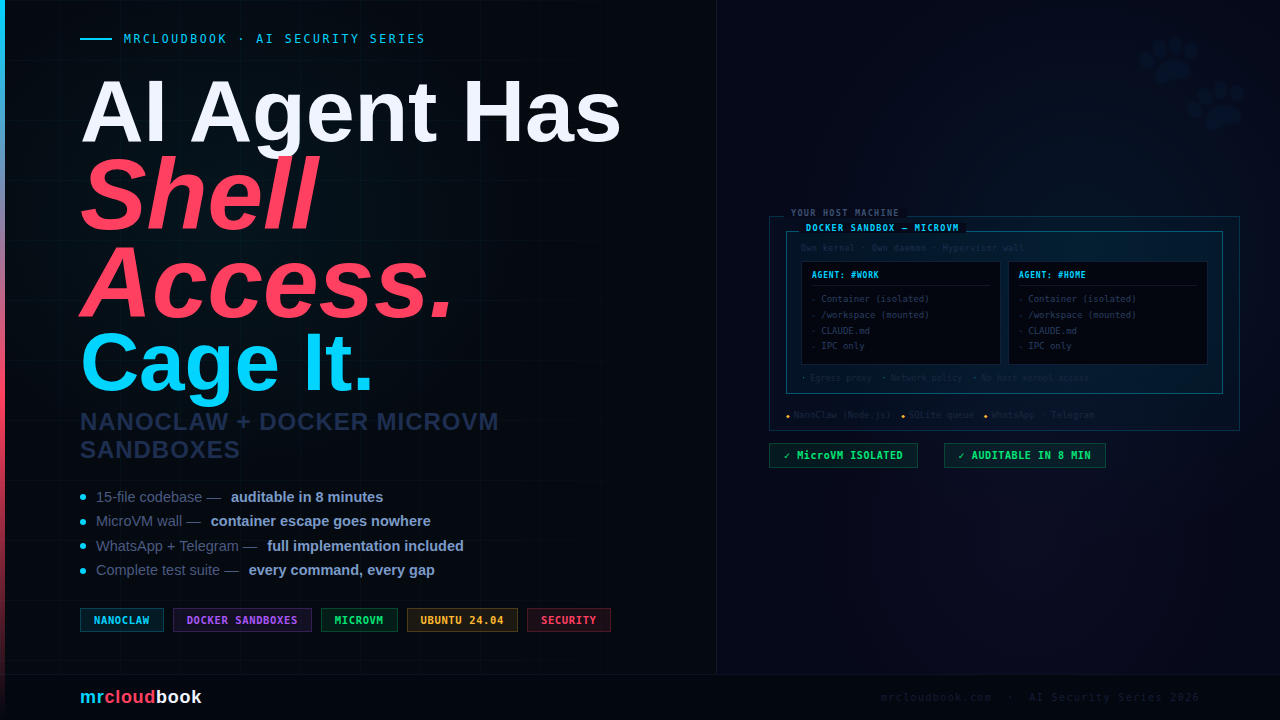
NanoClaw hit Hacker News this week, 134 points, and the DevSecOps reflex kicked in immediately - skepticism. Another AI agent framework that hallucinates destructive commands …